

Unified Identity Management
Connect enterprise AD and LDAP identity sources, manage users and application access centrally, and unify application authentication through OIDC. Keep accounts and permissions organized through onboarding, role changes and offboarding, with authentication event audits to help investigate access issues.
Core capabilities
Connect existing identity sources and manage users, application authentication and access permissions centrally, supported by certificate configuration and event auditing.
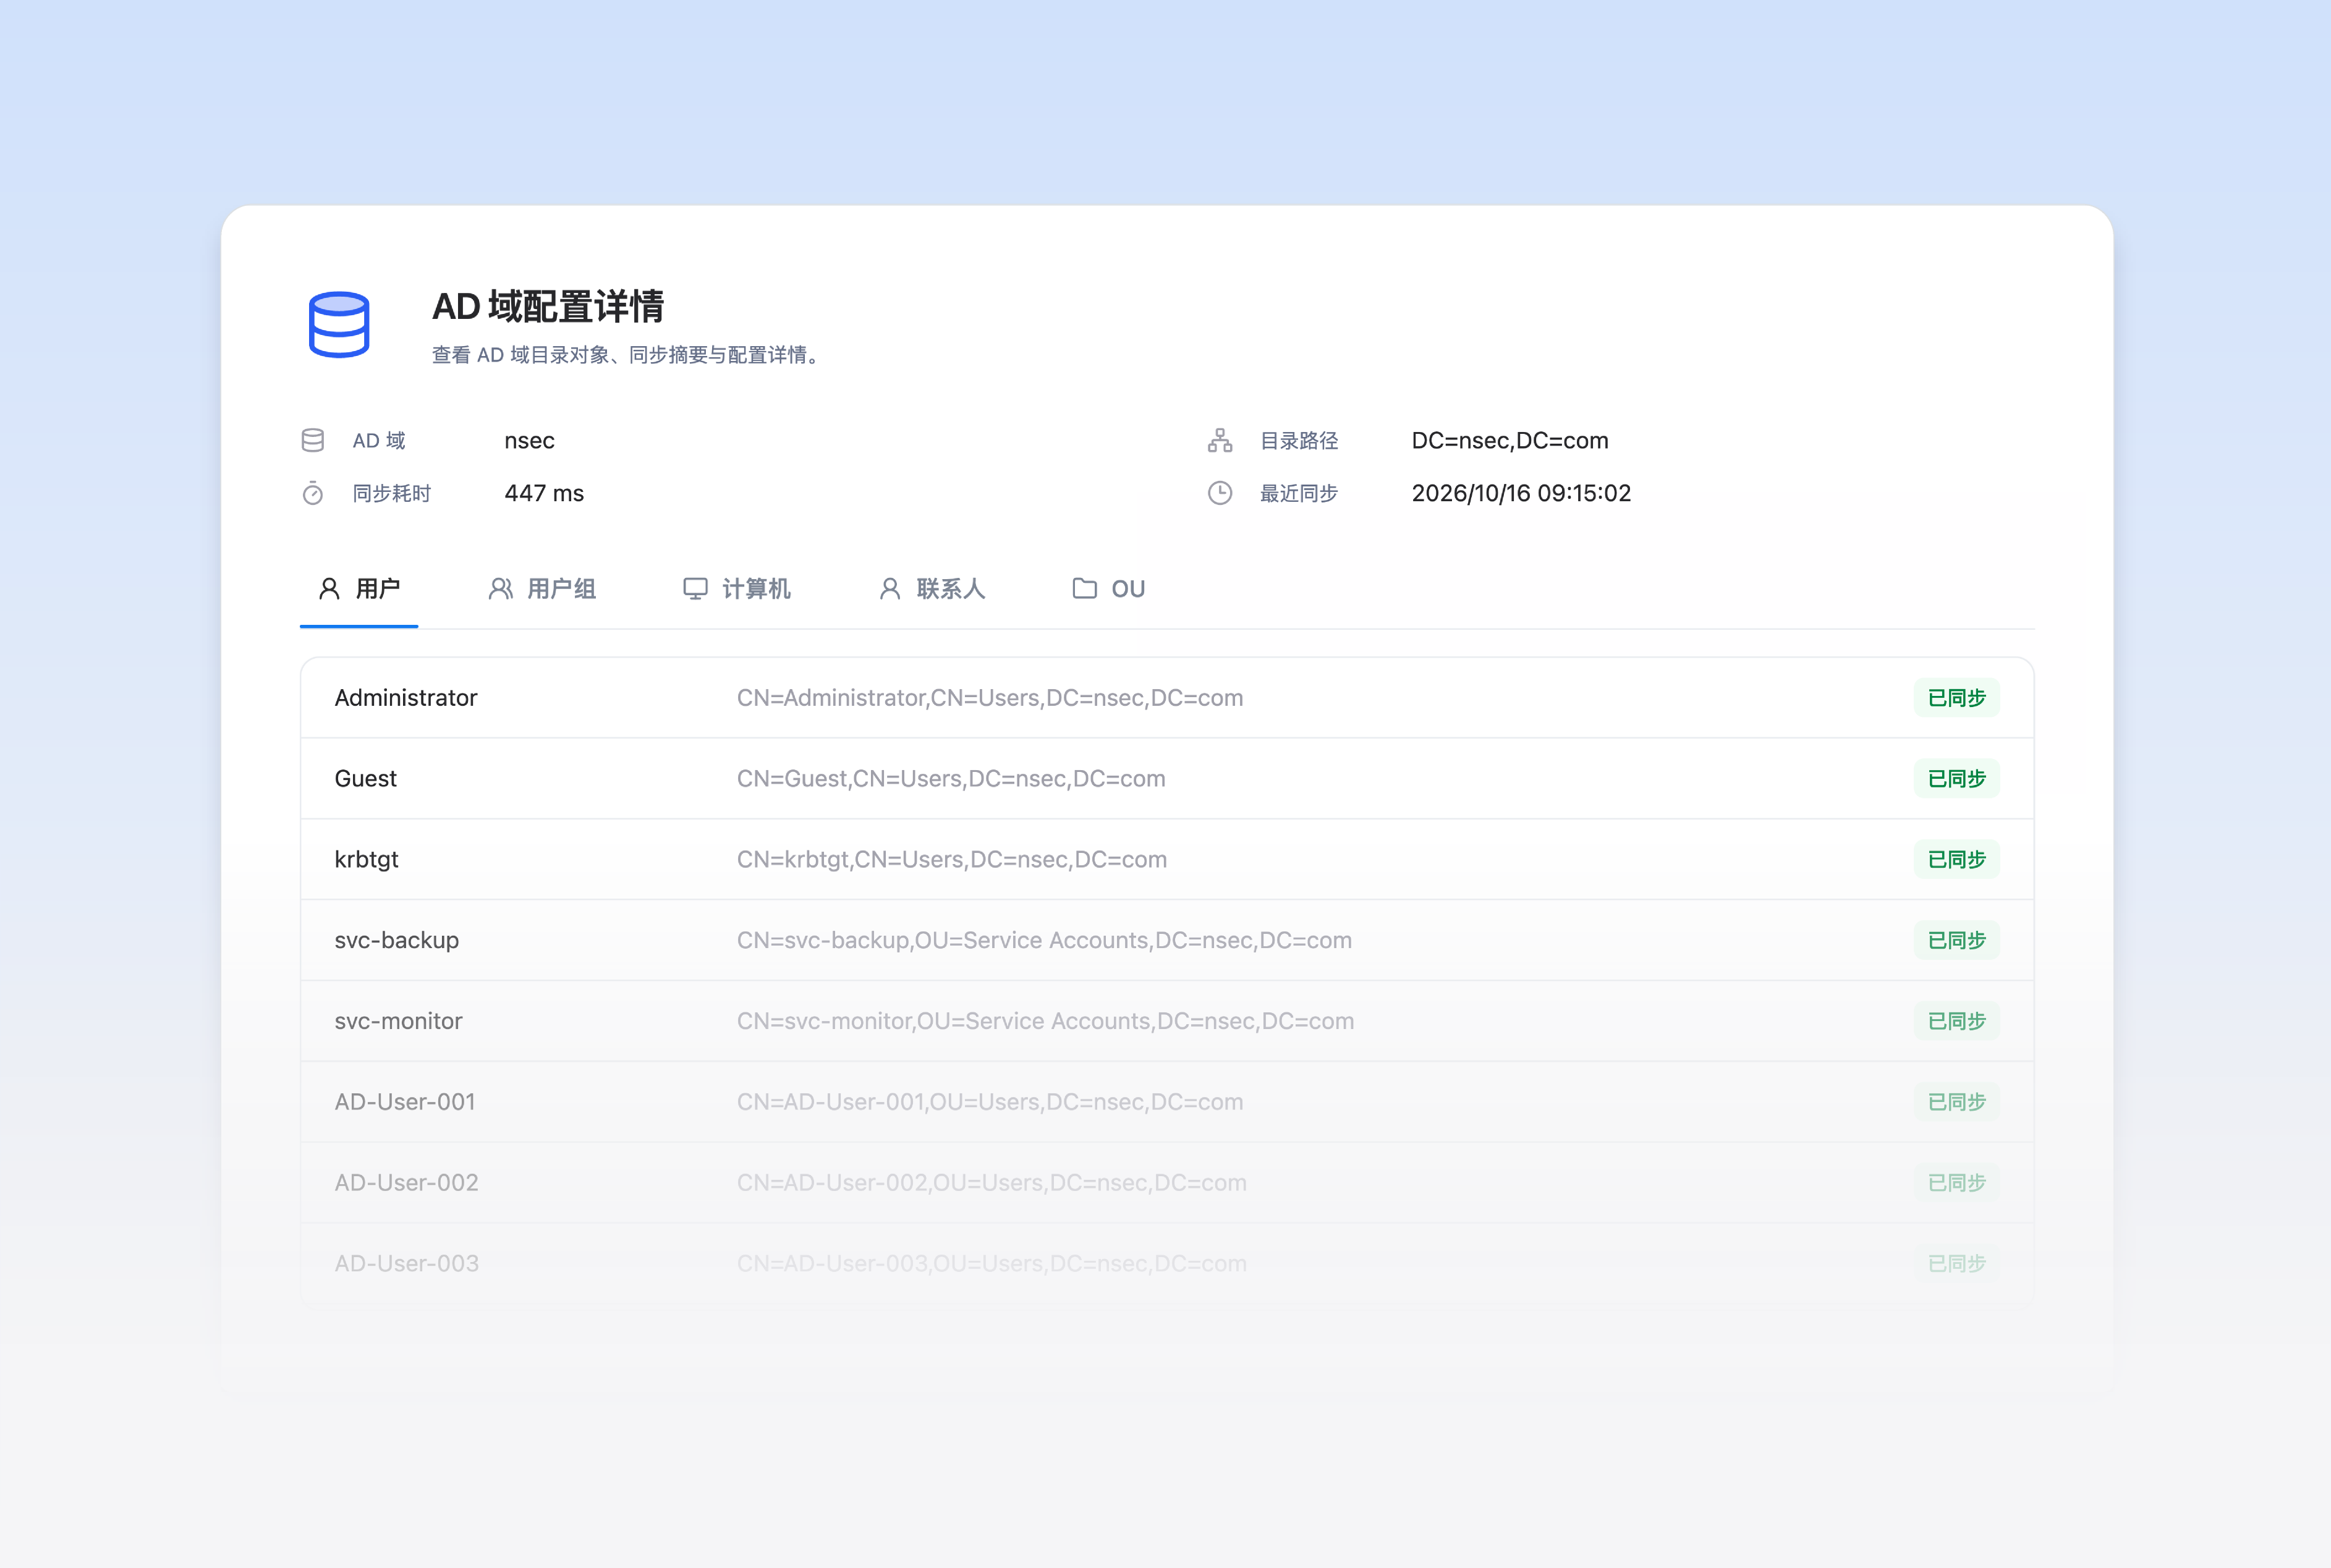
Identity sources and synchronization
Connect AD and LDAP, define sync scopes and schedules, and review directory sync status.
Unified user directory
Manage users, groups and identity sources.
 User identity
 OIDCApplication single sign-on
 Business apps
Application single sign-on
Connect apps through OIDC to handle sign-in and authorization in one flow.
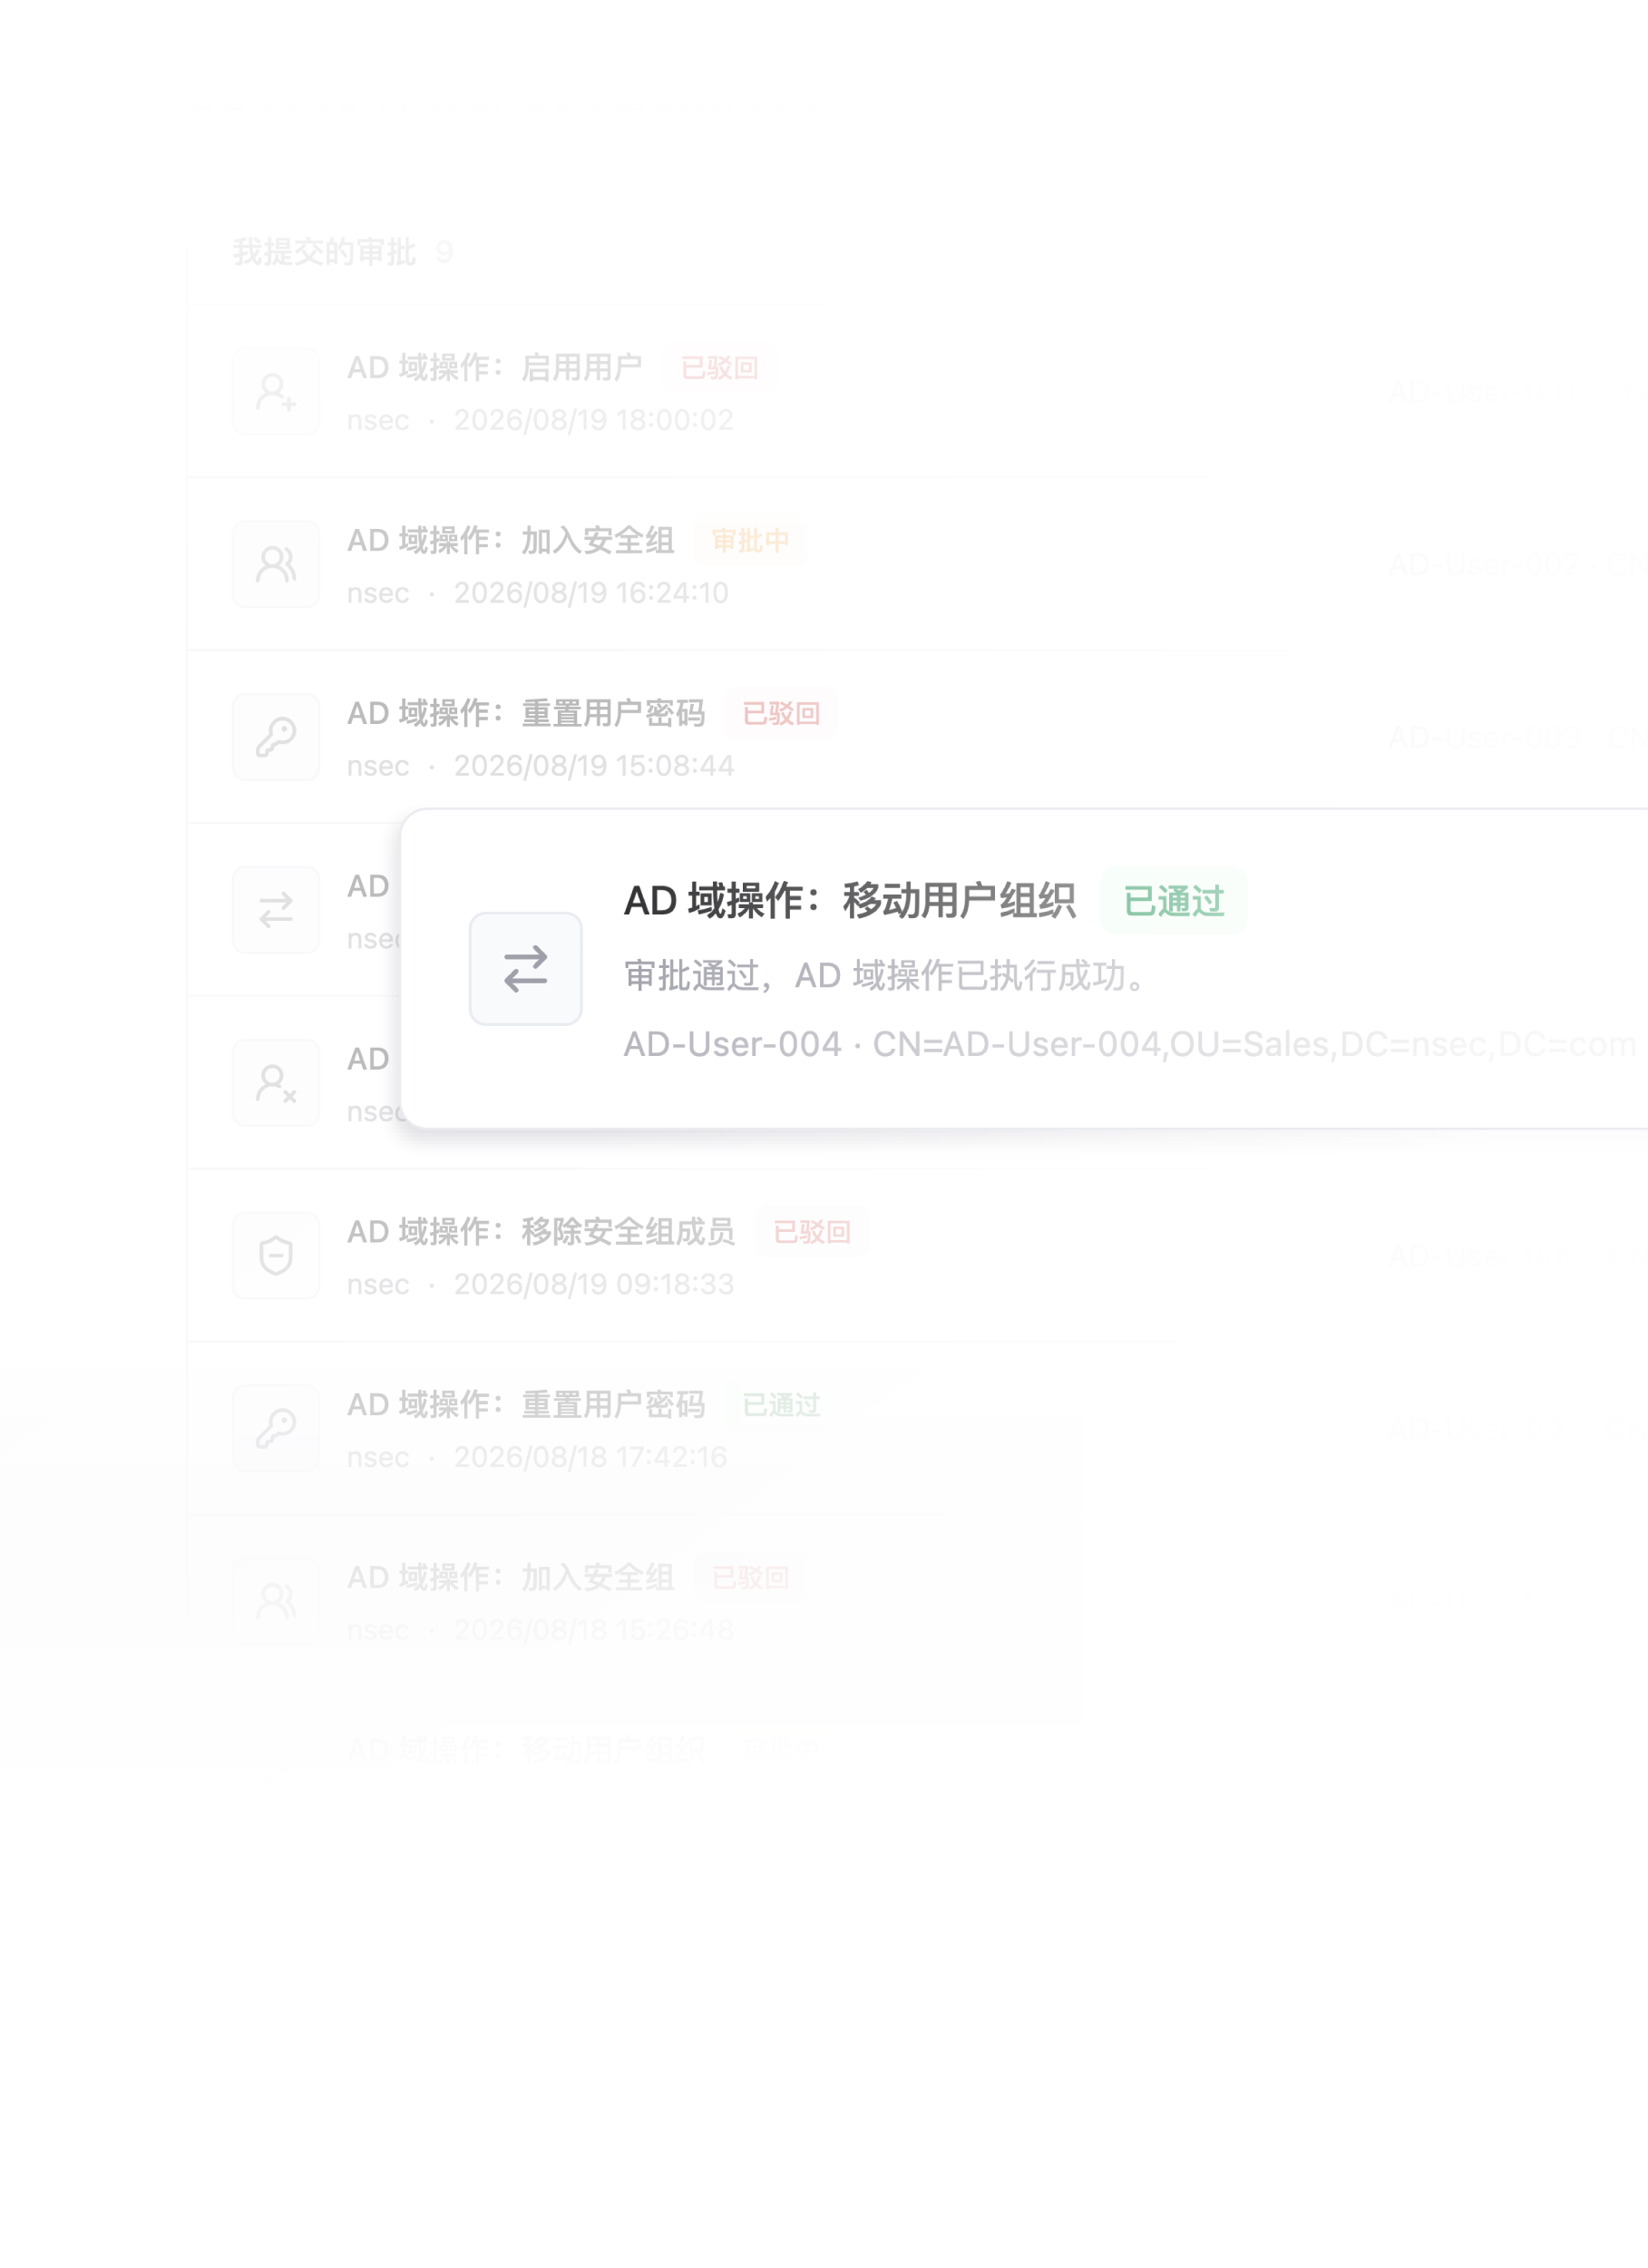
Application access control
Manage access scope for each app.
 Authentication and signing certificates
Maintain authentication settings and signing certificates for application integrations.

Authentication event audit
Review events by account and app.
Trace authentication from login to authorization
Connect login, authentication, authorization and callback events with account, application and outcome details. Trace the access process and investigate failed stages to understand login and authorization issues.
Review login and authentication events alongside account and application information to check the outcome.
Distinguish authorization requests from consent events when investigating application access.
Inspect token issuance and refresh events to locate problems in application authentication.
Review callback, completion and failure stages to trace how an authentication flow ended.
Clear identity sources, clear management boundaries
Identities may come from an existing directory or be created locally. Bring both into one view while preserving their sources and maintenance methods, providing context for account reviews, updates and application access.
Directory-synced identities
Connect AD and LDAP to sync identities and review scopes and task status.
Locally managed accounts
Create accounts and maintain user details, groups and application access.
A clear path from application setup to access
Connect application details, authentication settings and access scopes, then review sign-in events to understand how each integration works.
Register applications
Maintain application names and details in a central application directory.
Configure authentication
Set OIDC parameters and callback URLs to connect application sign-in.
Assign access
Maintain access scopes and review which users can access each application.
Review sign-ins
Inspect authentication and authorization events to investigate access issues.
Identity management in practice
From directory integration to onboarding, role changes and offboarding, manage identities, applications and access, and investigate sign-in issues through authentication events.
Connect an existing directory
Connect AD and LDAP to review identity sync scopes and directory objects.
Connect application sign-in
Connect business apps and configure authentication and callback URLs.
Onboard a colleague
Create or sync employee identities and assign the app access needed for work.

Adjust a role
Review application scopes as roles change and adjust access permissions.

Revoke departing users’ access
Review departing staff accounts and revoke application access no longer needed.
Investigate sign-in issues
Link accounts to application events to investigate sign-in and access issues.
Connect to your existing identity environment
Start with directory connectivity and application compatibility. Define where account and access management responsibilities begin and end.


